Technology
Chainalysis Says Breach Exposed Password Hashes and Live Tokens for All Users; Reactor, KYT Back Online
Chainalysis restored its Reactor, KYT and address screening products on November 7 after a breach that it says exposed names, usernames, password hashes and live tokens for all users.
What CISA, Project Zero and the CVE Program Say Happens Between Flaw Report and Advisory
Researchers, vendors and CVE numbering authorities move a software flaw through private triage, patching and public release, with timing that varies by program.
Linux Kernel TCP Flaw CVE-2026-98432 Has No Ubuntu Fix Yet; Go Cites Exploit
A Linux kernel TCP flaw rated 9.8 still had no Ubuntu fix as of 30 October, and a Go Security Team notice cites an exploit described by Anthropic.
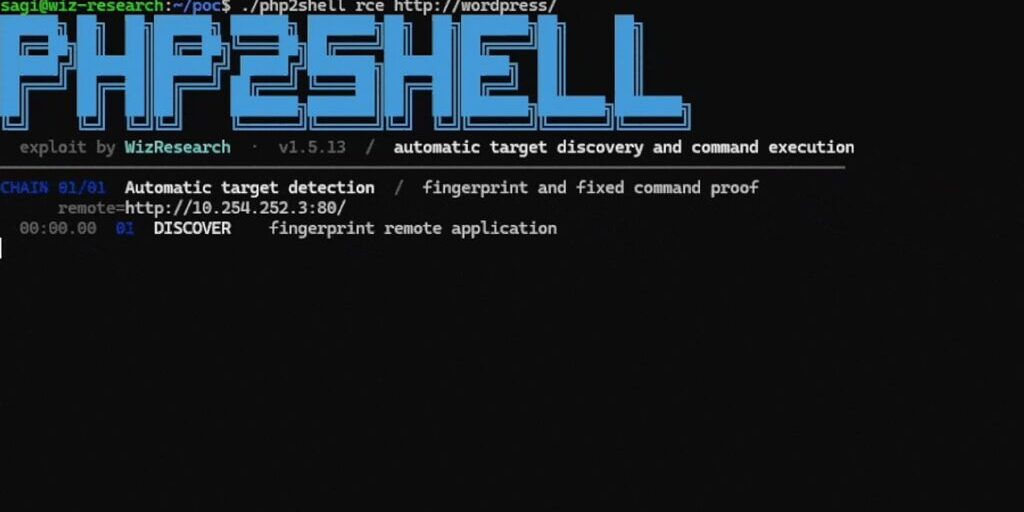
How the PHP2Shell Flaws Reached CISA’s Exploited List and What Patching Requires
Two unauthenticated PHP runtime flaws rated 9.2 now sit on CISA’s exploited list, and the fixes run from PHP 8.2.35 through 8.5.12.
Kaspersky Reports BlackX Bootkit Bypassing Secure Boot on Patched Windows PCs
Kaspersky says the BlackX bootkit, described in a 22 October 2026 report, exploits a Windows boot flaw that stays open on fully patched machines until revocation steps are run.
Why Chrome and Firefox Blocked Eight eMudhra Intermediate Certificates Within Hours
Browsers blocked eight eMudhra intermediate certificates within hours of a 17 October report. Here is how the keys were worked out and who faced risk.
Taiwan Plans Criminal Penalties for Unlicensed AI Chip Exports to China
Taiwan plans to make unlicensed exports of advanced AI chips and servers to China a criminal offence, Economy Minister Kung Ming-hsin said.
What FIDO2 Passkeys Keep on the Device, and What Depends on the Account Provider
Passkeys replace passwords with a key pair. The private key stays on the device, and syncing depends on the account provider a user chooses.