What China’s New Cyberspace Rules Let Police Inspect Starting October 1
China's Ministry of Public Security's new rules that took effect October 1 grant expanded powers to inspect tech companies on data, algorithms, and network security.
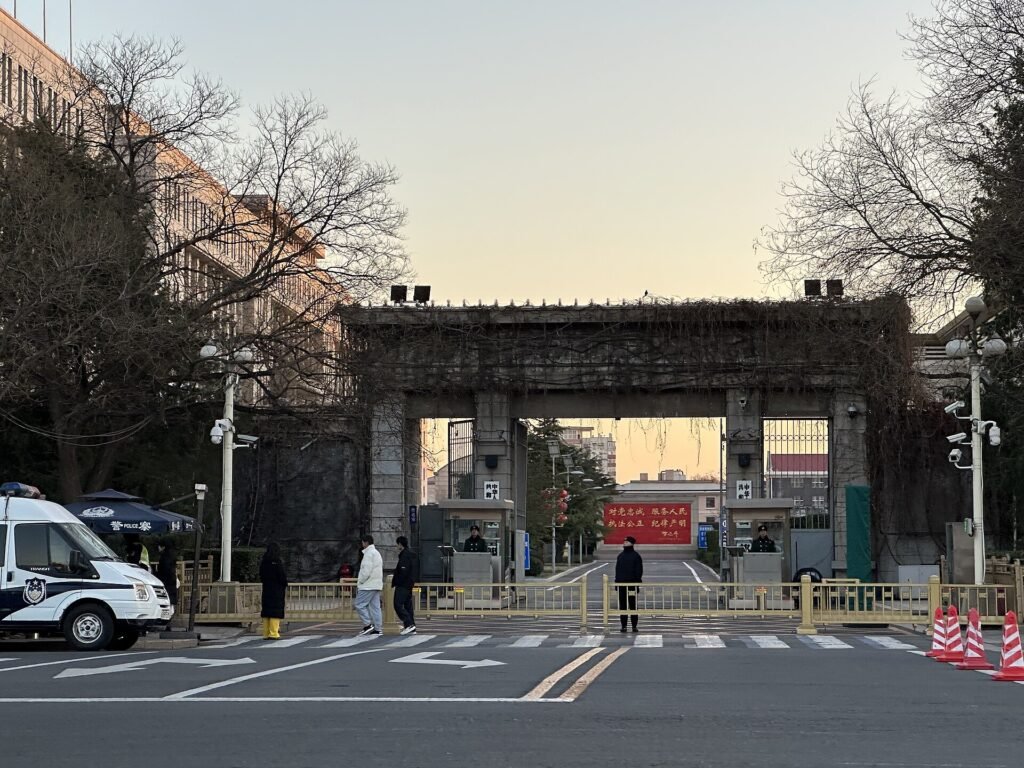
China’s Ministry of Public Security issued new Measures for Public Security Organs’ Supervision and Inspection of Cyberspace Security on August 6, 2026, and the rules took effect October 1, 2026. The framework replaces 2018 provisions on internet security oversight and expands police authority to inspect internet service providers, data processors, software vendors, and critical information infrastructure operators for compliance with China’s cybersecurity and data protection regime. The shift reflects what regulatory experts describe as a transition from monitoring to active control of network security.
The new rules establish two inspection processes: online monitoring and on-site inspections. Online monitoring includes network patrols, information-review capability testing, and vulnerability scanning, and can proceed without disrupting business operations. Capability testing requires three working days’ advance notice. On-site inspections are conducted by county-level and higher authorities, who must present credentials and written notice. Routine on-site visits are capped at one annual inspection for networks classified as Level 3 or above under China’s Multi-Level Protection Scheme, and for critical information infrastructure operators.
Shift from prior rules
The new 2026 Measures introduce significant procedural changes. On-site inspections now require written notice and are limited to one routine visit per year for major networks. The scope also expands: where the 2018 rules focused on traditional internet safety, the 2026 Measures explicitly bring data processing, personal information handling, and algorithm recommendation systems within the security inspection regime.
The regulations apply equally to internet service providers, public internet access venues, network operators and their contractors, critical information infrastructure operators, software product vendors, data handlers, and personal information handlers. The measures do not distinguish between domestic Chinese companies and foreign operators in listing which entities are subject to inspection. Organizations with prior security incidents or unresolved compliance violations face heightened scrutiny and priority inspections.
The rules
China’s Ministry of Public Security issued the Measures for Public Security Organs’ Supervision and Inspection of Cyberspace Security on August 6, 2026, effective October 1, 2026, replacing 2018 provisions. On-site inspections are capped at one routine visit per year for Level 3 or higher networks.
Compliance obligations and reporting
The regulations require compliance across eleven focus areas: network access filing, internal security management systems, user registration and internet log retention, multi-level protection scheme compliance, critical infrastructure safeguards, technical defenses against intrusion and malware, vulnerability remediation, content controls, algorithm recommendation governance, data and personal information protection, and cooperation with police on national security, counter-terrorism, and criminal investigations. Companies must implement comprehensive cybersecurity management programs, maintain documentation of security measures, and conduct regular risk assessments.
Companies face strict incident reporting requirements under a separate CAC regulation in force since November 2025. Network operators other than critical information infrastructure operators must report data breaches classified as “Relatively Severe or above” to China’s Cyberspace Administration within four hours of discovery, including incident details and remedial measures; critical information infrastructure operators must report within one hour to their sector regulator and police. The revised Chinese Cybersecurity Law, which took effect January 1, 2026, introduced substantially higher administrative fines and personal liability for executives, including chief security officers and Personal Information Protection Officers. Regulators employ multiple enforcement mechanisms: informal inquiries, on-site inspections, rectification orders, and formal investigations.
Inspection procedures and enforcement
Police can conduct remote technical testing, including vulnerability probing and penetration testing, with three days’ advance notice. Police are authorized to engage third-party technical providers to conduct inspections, though police retain direct control over the process. If authorities discover risks and hidden dangers in cybersecurity, information security, data security, or other areas during inspections, they may direct companies to remedy the issues.
Inspection findings can be shared with China’s Cyberspace Administration and other regulators, potentially triggering additional enforcement actions. Companies demonstrating proportionate technical and organizational controls through permits, certifications, audits, and structured compliance processes develop stronger affirmative defences in enforcement actions. Cross-border data transfers face restrictions: data handlers cannot transfer personal information or important data overseas without security assessments or standard contractual clauses, depending on data volume thresholds. In an October 2025 Q&A, the Cyberspace Administration clarified that international systems, such as hotel reservation platforms, do not automatically satisfy legal requirements for transferring Chinese resident data.
Routine on-site visits are capped at one annual inspection for networks classified as Level 3 or above, and for critical information infrastructure operators.
Next steps for companies
The rules are now in effect with no grace period for compliance. Inspections can begin immediately. American technology companies operating in China should ensure their documentation of compliance measures is current and their security infrastructure aligns with the eleven required areas. The Multi-Level Protection Scheme, which remains foundational to compliance, requires tiered security defenses appropriate to the sensitivity of data handled. Organizations should conduct data inventories, create records of processing activities aligned with regulatory requirements, and establish incident response procedures that meet the four-hour reporting deadline for severe breaches.
Related coverage: What New York City’s Local Law 144 Requires of AI Hiring Tools; How EvilTokens Used AI to Breach 12,000 Corporate Inboxes.
Photo: Zheng Zhou · CC BY-SA 4.0 · via Wikimedia Commons